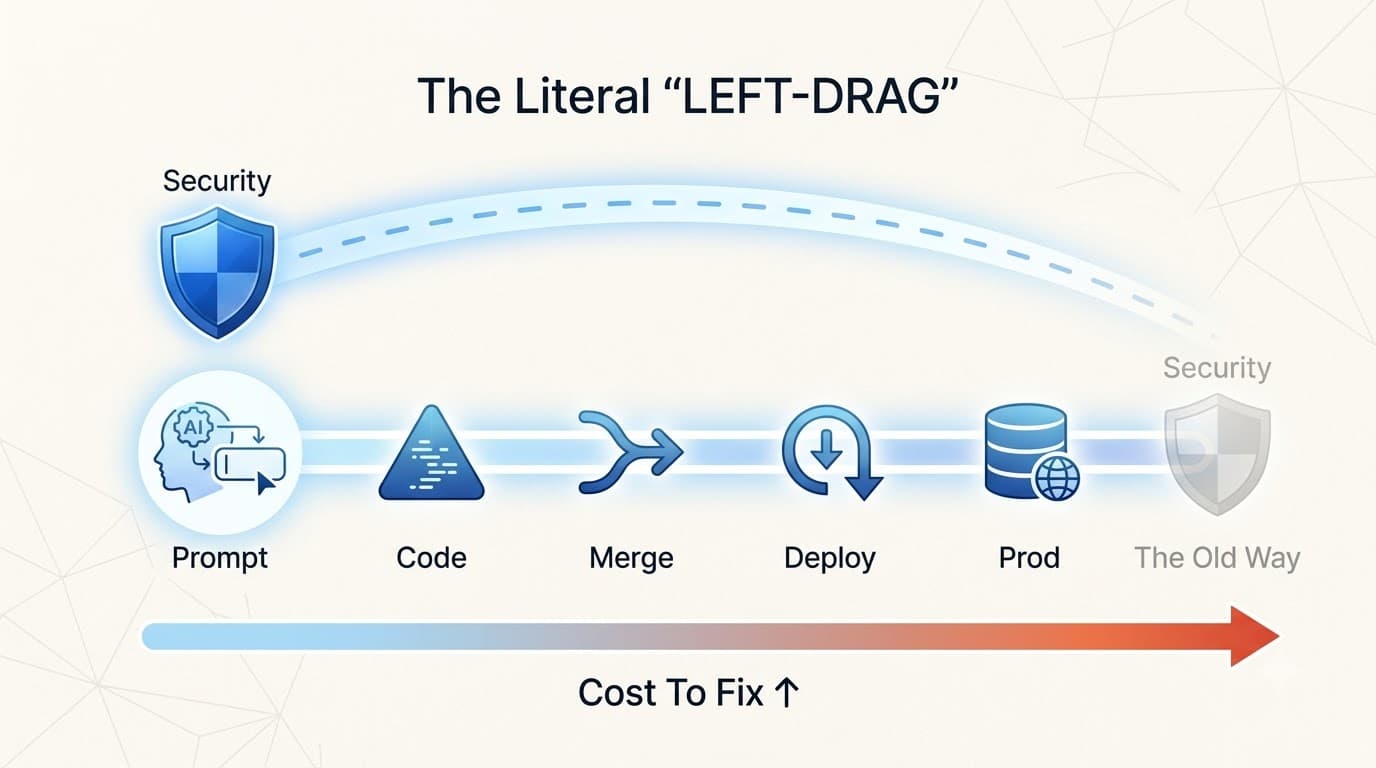
AI now lets developers generate code, tests, agents, and whole workflows from a prompt. But security practices built for human-written code and slower cycles don’t scale to that speed. Bolting security on at the end hurts quality and stalls delivery, so security has to shift left: start at the earliest stage and stay in place throughout. In the AI era, that means deciding what to validate, when, and how to build confidence in generated output.
The 5 Principles
1. Trust the outcome, not just the generation
AI-generated code often compiles, runs, and passes tests, yet still hides risk. Working code isn’t the same as secure code. Check for:
- Over-broad permissions and data access
- Data leaks or exfiltration
- Behavior when authentication fails (fail safe vs. fail open)
- Damage from malformed or corrupt input
The question to ask is not “does it work?” but “does it behave securely in real-world conditions?“
2. Start security during development
Security reviews at the end of the process never worked well, and they fail even more when code can be generated in seconds. Bugs are cheapest to fix early and most expensive in production. Build checks into the workflow as code is written:
- Static and dynamic analysis, and penetration testing
- Secrets scanning
- Policy and compliance checks
3. Scrutinize dependencies
AI also brings in new packages, libraries, services, and integrations, each of which adds capability and risk. Developers tend to review generated code and overlook what it pulls in, yet many incidents start in the software supply chain. Vet generated dependencies as carefully as generated code:
- Package reputation and known vulnerabilities
- Licensing and source integrity
- Alignment with organizational standards
4. Validate intent, not just code
Many security failures come from wrong assumptions, not bad coding. Code can be elegant and still violate policy if the requirements were misunderstood. For example, a workflow may process financial data correctly while exposing it to people who should never see it. Be explicit about who can access what, which actions are allowed, which business rules apply, and what must stay protected. Reviewing AI output now means asking whether it solved the right problem in the right way.
5. Make security continuous
AI produces constant change, so validation must be constant too, across the whole loop of develop → test → deploy → monitor → improve. That includes:
- Ongoing vulnerability detection, including with frontier AI models
- Dependency monitoring and patching
- Policy enforcement and change validation
The question is not “did it pass once?” but “does it keep passing?” A frontier AI model recently uncovered a zero-day that had sat in an open-source operating system for 27 years, a reminder that security is never finished.
Securing AI Agents
As agents take on multi-step work across services, repos, pipelines, and configs, reviewing individual files is no longer enough. The hardest problems come from unintended consequences across connected systems. Agents need:
- Guardrails defining what they can and can’t do
- Identities so their actions are traceable and accountable
- Access controls that limit what they can change
- Monitoring and human-in-the-loop oversight
Without these, agents become risk amplifiers instead of productivity tools.
Bottom Line
More generated code means more functionality, but also more complexity, and complexity is the enemy of security. Speed alone doesn’t create value; trust does. The winning organizations will build security into everyday workflows as continuous validation, not a compliance exercise or release gate. The goal is to verify outcomes with confidence across a growing codebase, faster than ever.